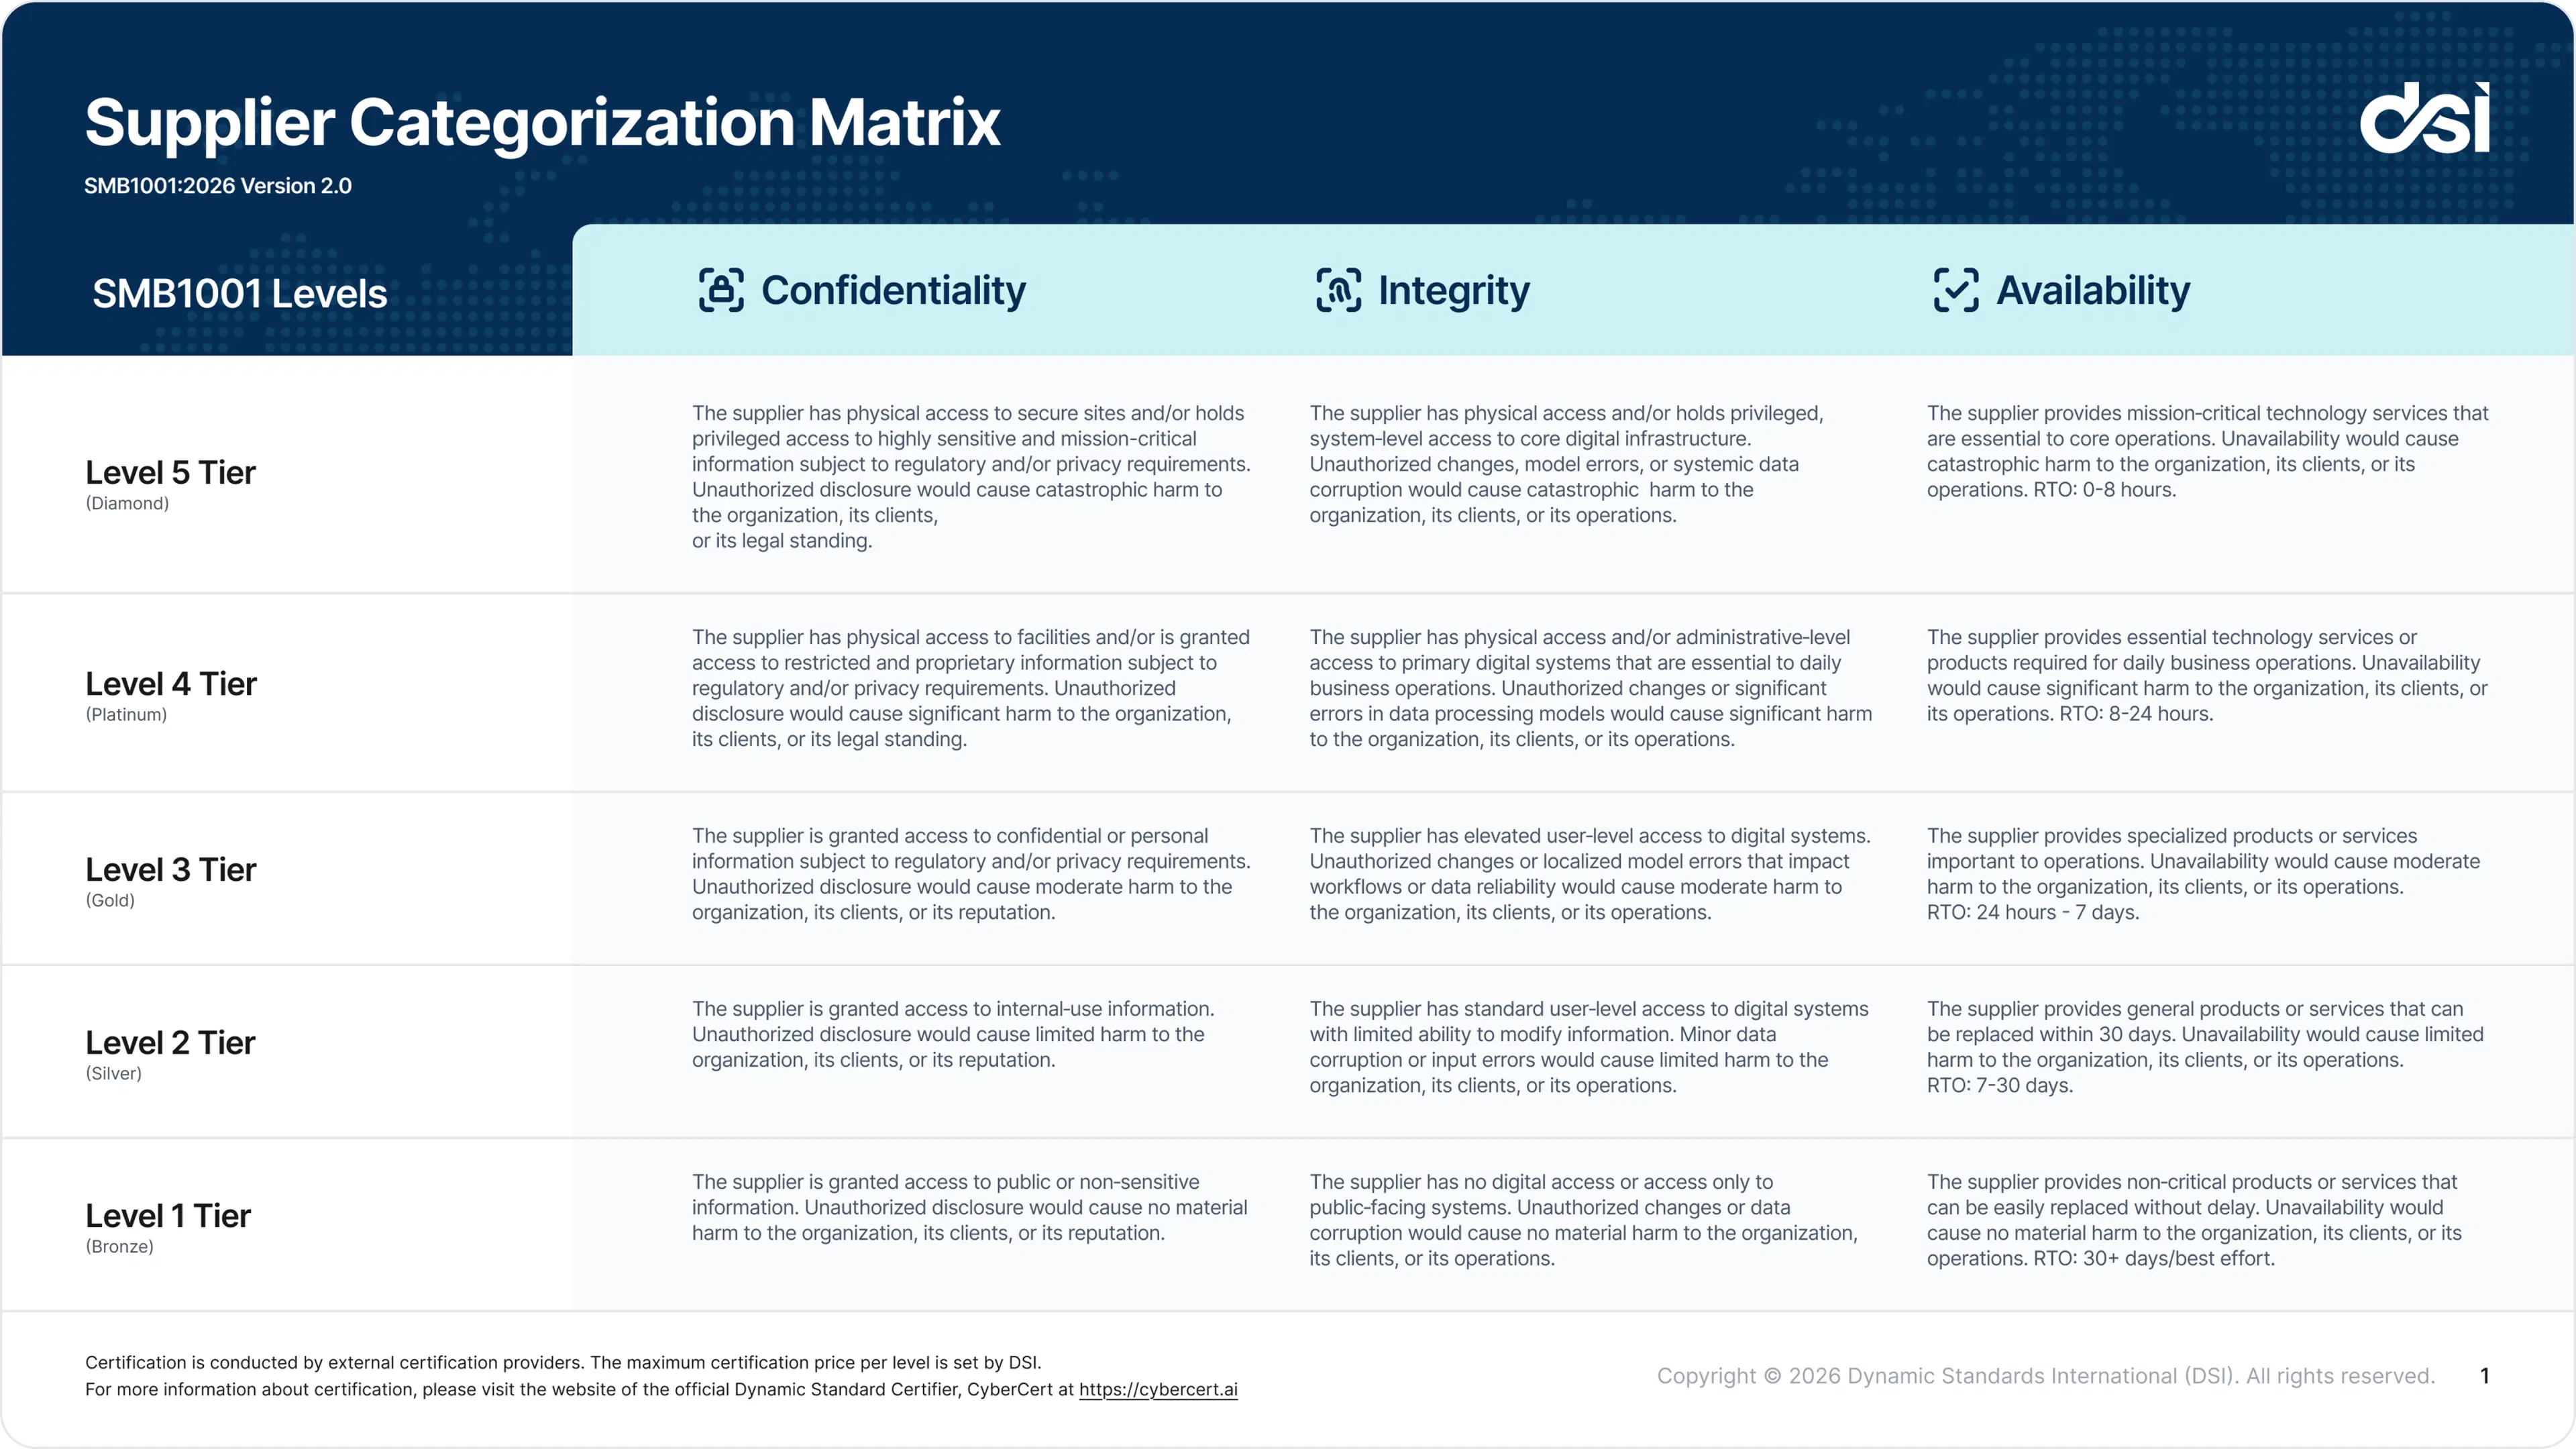
Building on the SMB1001 standard, DSI's Supplier Categorization Matrix determines the appropriate SMB1001 level for businesses based on confidentiality, integrity, availability, and related threats.
Typical enterprise supply chains comprise of a large variety of supplier types, and their corresponding security needs may differ. Within the industry, many supply chain solutions still treat all suppliers uniformly, without consideration of their information security context.
Building on the SMB1001 standard, DSI has developed a Supplier Categorization Matrix which provides a way to determine the appropriate SMB1001 level for a business based on three factors:
the information they store,
the access they have, and
their type of goods/service they provide.

As an additional benefit enabling supplier conversations, the matrix links these three factors with potential threats and relevant controls. It is easy for suppliers to see how the information they process, the access they have, and what they do may expose them to threats and the controls in SMB1001 that can help manage these threats.
Not all suppliers have the same appetite or need for cyber security. Similarly, not all suppliers need to meet the same level of SMB1001. Our Supplier Categorization Matrix acknowledges this need for varied advice by providing a way to identify the relevant SMB1001 level for businesses based on three pillars of confidentiality, integrity and availability and the associated threats.
Confidentiality refers to the type of information the supplier handles. For example, suppliers accessing protected information may require Platinum-level certification under SMB1001 to safeguard sensitive data on remote-access systems.
Integrity assesses the level and type of access the supplier has. Suppliers without digital system access may only need Bronze-level certification, while those with higher access privileges need advanced security measures.
Availability considers how critical the supplier’s services are. Suppliers offering essential technology services, where downtime must not exceed 8 hours, may require Diamond-level certification to ensure proper incident response and backup protocols are in place.
DSI's Supplier Categorization Matrix aligns SMB1001 levels with suppliers' roles, potential threats, and necessary controls based on three critical factors, confidentiality, integrity, and availability.
The following matrix helps governments and enterprises determine the appropriate certification levels for their SMB suppliers, balancing their capabilities with the level of risk they pose within the supply chain.

Customer Profile
The SMB does not have any access to the organization’s systems i.e. the organization is just a customer without needing long-term interaction or sharing of information.
Certification Details
Bronze
Director attested
Confidentiality
Integrity
Availability
Risk Exposure
Confidentiality
The supplier is granted access to public or non-sensitive information. Unauthorized disclosure would cause no material harm to the organization, its clients, or its reputation.
Integrity
The supplier has no digital access or access only to public-facing systems. Unauthorized changes or data corruption would cause no material harm to the organization, its clients, or its operations.
Availability
The supplier provides non-critical products or services that can be easily replaced without delay. Unavailability would cause no material harm to the organization, its clients, or its operations. RTO: 30+ days/best effort.
Representative Key Threats
Confidentiality
Integrity
Availability
Key Controls
Confidentiality
Integrity
Availability
Customer Profile
The SMB has typical access to the organization’s systems and has received or sent corporate information.
Certification Details
Silver
Director attested
Confidentiality
Integrity
Availability
Risk Exposure
Confidentiality
The supplier is granted access to internal-use information. Unauthorized disclosure would cause limited harm to the organization, its clients, or its reputation.
Integrity
The supplier has standard user-level access to digital systems with limited ability to modify information. Minor data corruption or input errors would cause limited harm to the organization, its clients, or its operations.
Availability
The supplier provides general products or services that can be replaced within 30 days. Unavailability would cause limited harm to the organization, its clients, or its operations. RTO: 7–30 days.
Representative Key Threats
Confidentiality
Integrity
Availability
Key Controls
Confidentiality
Integrity
Availability
Customer Profile
The SMB is a supplier for an organisation with administrator or other access to personal and sensitive information.
Certification Details
Gold
Director attested
Confidentiality
Integrity
Availability
Risk Exposure
Confidentiality
The supplier is granted access to confidential or personal information subject to regulatory and/or privacy requirements. Unauthorized disclosure would cause moderate harm to the organization, its clients, or its reputation.
Integrity
The supplier has elevated user-level access to digital systems. Unauthorized changes or localized model errors that impact workflows or data reliability would cause moderate harm to the organization, its clients, or its operations.
Availability
The supplier provides specialized products or services important to operations. Unavailability would cause moderate harm to the organization, its clients, or its operations. RTO: 24 hours – 7 days.
Representative Key Threats
Confidentiality
Integrity
Availability
Key Controls
Confidentiality
Integrity
Availability
Customer Profile
The SMB is a critical supplier for an organisation with physical access and administrator access.
Certification Details
Platinum
Director Attested / Audited
Confidentiality
Integrity
Availability
Risk Exposure
Confidentiality
The supplier has physical access to facilities and/or is granted access to restricted and proprietary information subject to regulatory and/or privacy requirements. Unauthorized disclosure would cause significant harm to the organization, its clients, or its legal standing.
Integrity
The supplier has physical access and/or administrative-level access to primary digital systems that are essential to daily business operations. Unauthorized changes or significant errors in data processing models would cause significant harm to the organization, its clients, or its operations.
Availability
The supplier provides essential technology services or products required for daily business operations. Unavailability would cause significant harm to the organization, its clients, or its operations. RTO: 8–24 hours.
Representative Key Threats
Confidentiality
Integrity
Availability
Key Controls
Confidentiality
Integrity
Availability
Customer Profile
The SMB is a critical supplier to organizations, with physical or administrative access to the information.
Certification Details
Diamond
Director Attested / Audited
Confidentiality
Integrity
Availability
Risk Exposure
Confidentiality
The supplier has physical access to secure sites and/or holds privileged access to highly sensitive and mission-critical information subject to regulatory and/or privacy requirements. Unauthorized disclosure would cause catastrophic harm to the organization, its clients, or its legal standing.
Integrity
The supplier has physical access and/or holds privileged, system-level access to core digital infrastructure. Unauthorized changes, model errors, or systemic data corruption would cause catastrophic harm to the organization, its clients, or its operations.
Availability
The supplier provides mission-critical technology services that are essential to core operations. Unavailability would cause catastrophic harm to the organization, its clients, or its operations. RTO: 0–8 hours.
Representative Key Threats
Confidentiality
Integrity
Availability
Key Controls
Confidentiality
Integrity
Availability
Following the matrix, the first pillar is confidentiality. The supplier has access to confidential information from your business. This means that this information may be at risk if the supplier experiences a data breach, phishing or an insider threat. Hence, the supplier categorisation would be SMB1001 Silver level.
Though a similar categorisation would be made considering the integrity pillar as the supplier does not have administrator access, the supplier provides technology services important to the business. Hence, their ongoing availability is essential. Therefore, the supplier categorisation would change from Silver to Gold to account for the importance of ongoing availability. The supplier would then be categorised at SMB1001 Gold level.